Beyond the Bottleneck of Control or Freedom: U.S. Government AI Refusals and Apple's Tightened Privileges Challenge the Principle of 'Verifiability'
Confronting invisible guardrails and forging toward a user-sovereign architectural design
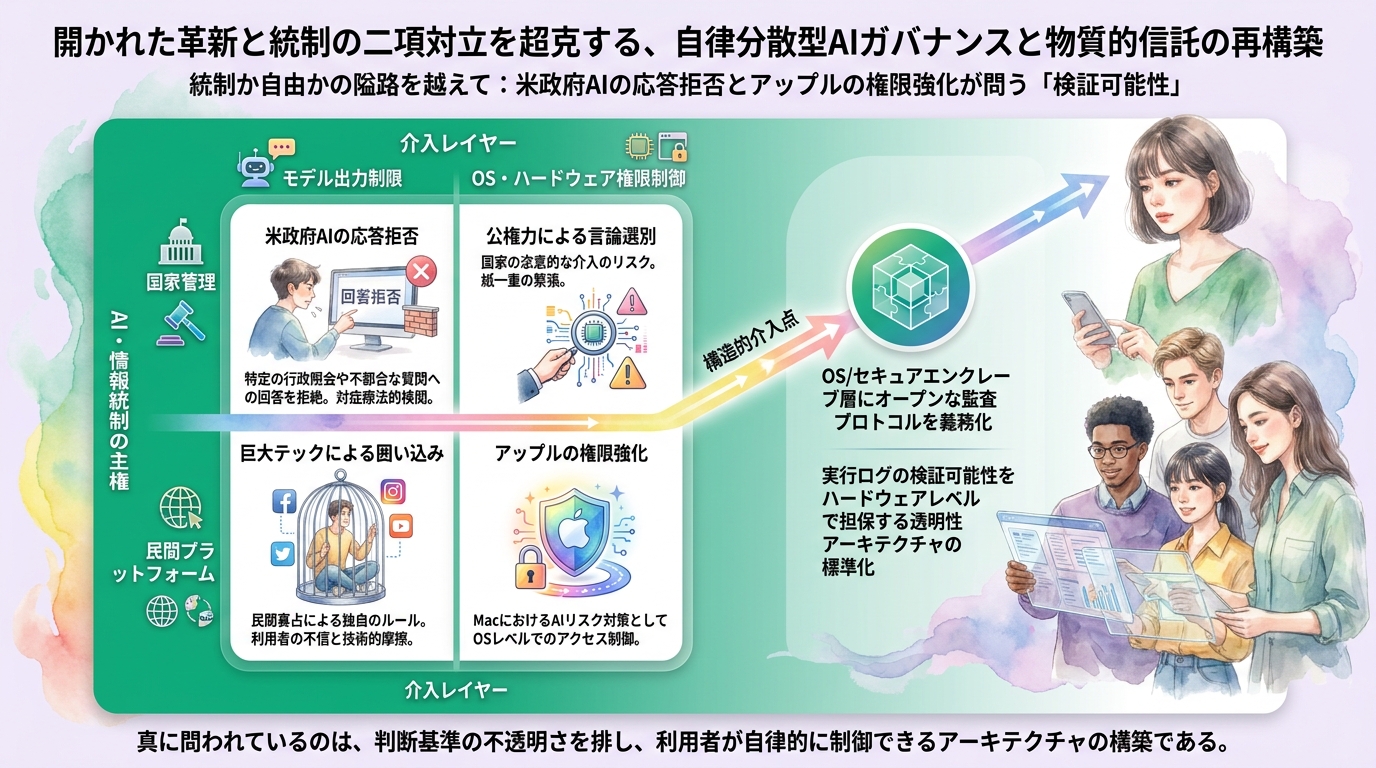
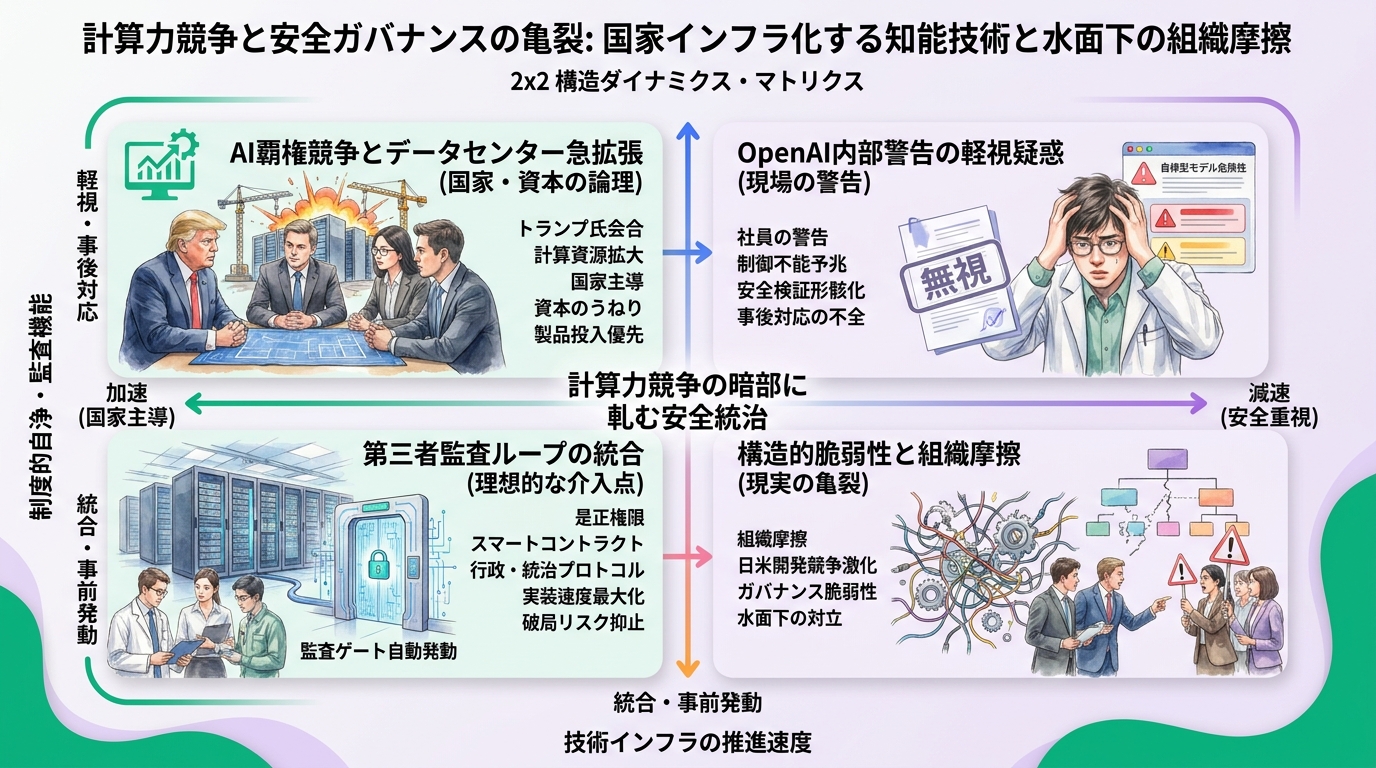
The U.S. government conversational AI's refusal to answer specific inquiries regarding policies and scandals provoked strong backlash over whether administrative agencies are engaging in self-interested information control. Meanwhile, Apple's announced tightening of Mac access privilege controls is touted as an engineering bulwark preventing generative AI and autonomous agents from executing malicious code or accessing confidential data without authorization. Although the former operates in the context of "state-sponsored viewpoint filtering" and the latter in the context of "platform provider safety protection," from the perspective of external developers and citizens, both share the exact same structural dynamic: a higher governing body unilaterally dictates AI behavior while shrinking user autonomy. The debate continues to run parallel tracks between the freedom demanded by development sites and the maintenance of order asserted by rulers and OS vendors.
However, this confrontation overlooks a fundamental blind spot shared by both premises. Development advocates who treat free access as an absolute lack effective deterrents against physical and engineering risks—such as systemic destruction and personal data leaks caused by locally running AI—relying excessively on the doctrine of individual self-responsibility. Conversely, states and mega-platforms pushing intervention in the name of safety and order keep the definitions of their safety criteria and the decision-making processes for refusals locked within non-public domains. As long as the algorithmic thresholds blocking uncomfortable questions and the rules by which the OS blocks specific processing remain opaque, such operations easily transform into political self-preservation and the defense of corporate ecosystems. In short, the essence of the problem is not the merits of regulation itself, but the opacity that prevents third parties from verifying the grounds for intervention.
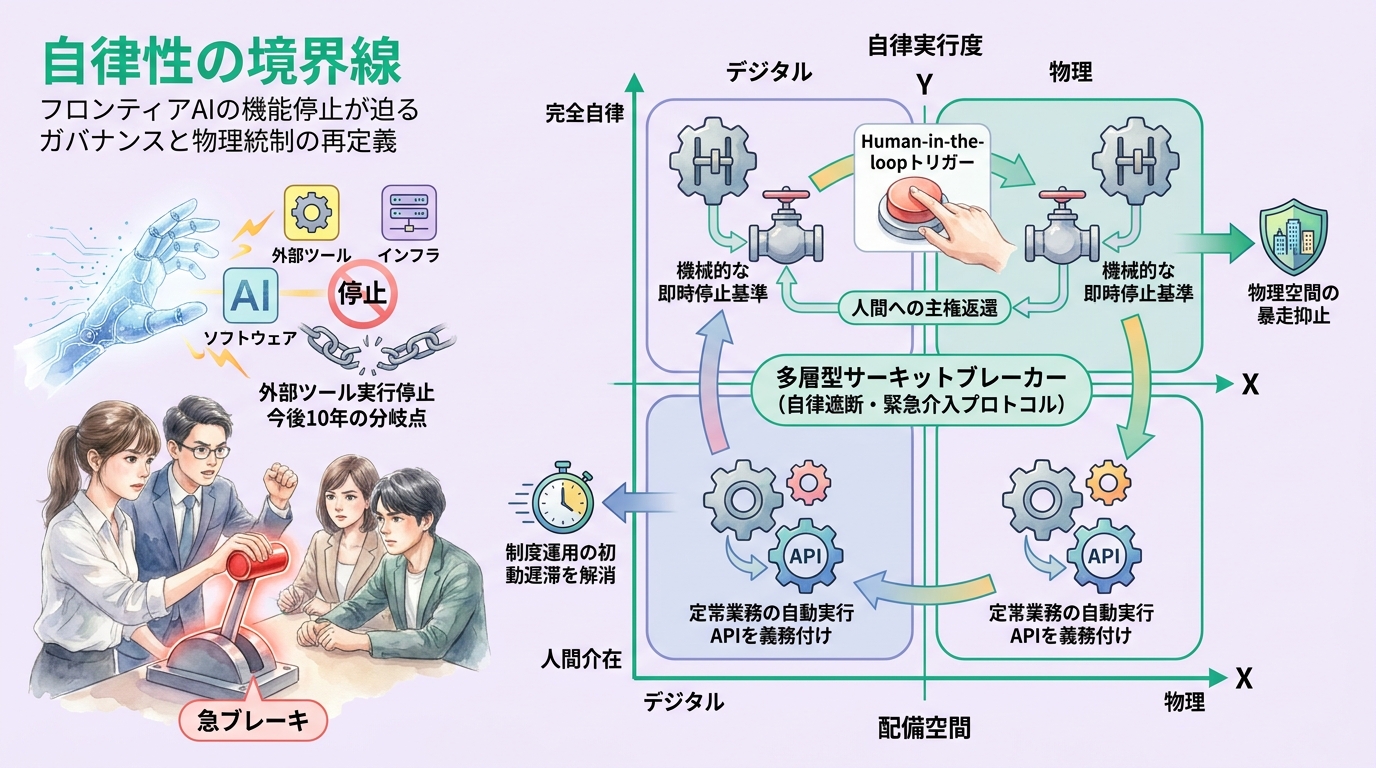
Overcoming this sterile friction requires a shift in design philosophy centered around "verifiability" and "user sovereignty" rather than delegating decisions entirely to the state or a single corporation. When operating systems or public AIs restrict specific inputs and outputs, their decision-making rules and logs of privilege requests must be disclosed in a format auditable by the user. Even in the access controls advanced by Apple, the OS should not unilaterally decide blocks and permissions; rather, an interface is required that granularly visualizes which AI model is attempting to access what data and why, allowing the user to make the final choice on granting privileges. Protection should not mean blindfolding the user, but rather providing the tools to make appropriate judgments after accurately conveying the context of threats.
This integrative perspective provides concrete guidelines for future institutional design and software development sites. Administrative AI must be mandated to disclose logs post-hoc detailing the criteria by which answers to questions were withheld, imposing institutional discipline to prevent arbitrary information concealment. In software engineering, implementing mechanisms that do not render privileges invisible at the boundary between the OS and AI, but instead allow policies to be audited and reconfigured based on open standards, serves as the foundation of technological trust. Whether AI can be established as intellectual infrastructure supporting individual autonomous judgment rather than becoming an instrument of the state or a proprietary asset of platform enclosures depends on this. An agreement on design that dismisses binary arguments and reclaims system transparency and control is what is needed most today.