The Reproducing Structure of State-Sponsored Crypto Crime: Breaking the Chain of $12.8 Billion in Illicit Outflows Fueling Weaponry Development and Reinvestment
Vulnerabilities in Cashing-Out Infrastructure Exposed by Cyberattack on GMO / Encirclement of the 'Off-Ramp', the Achilles' Heel of Sanction-Bypassing Money Laundering
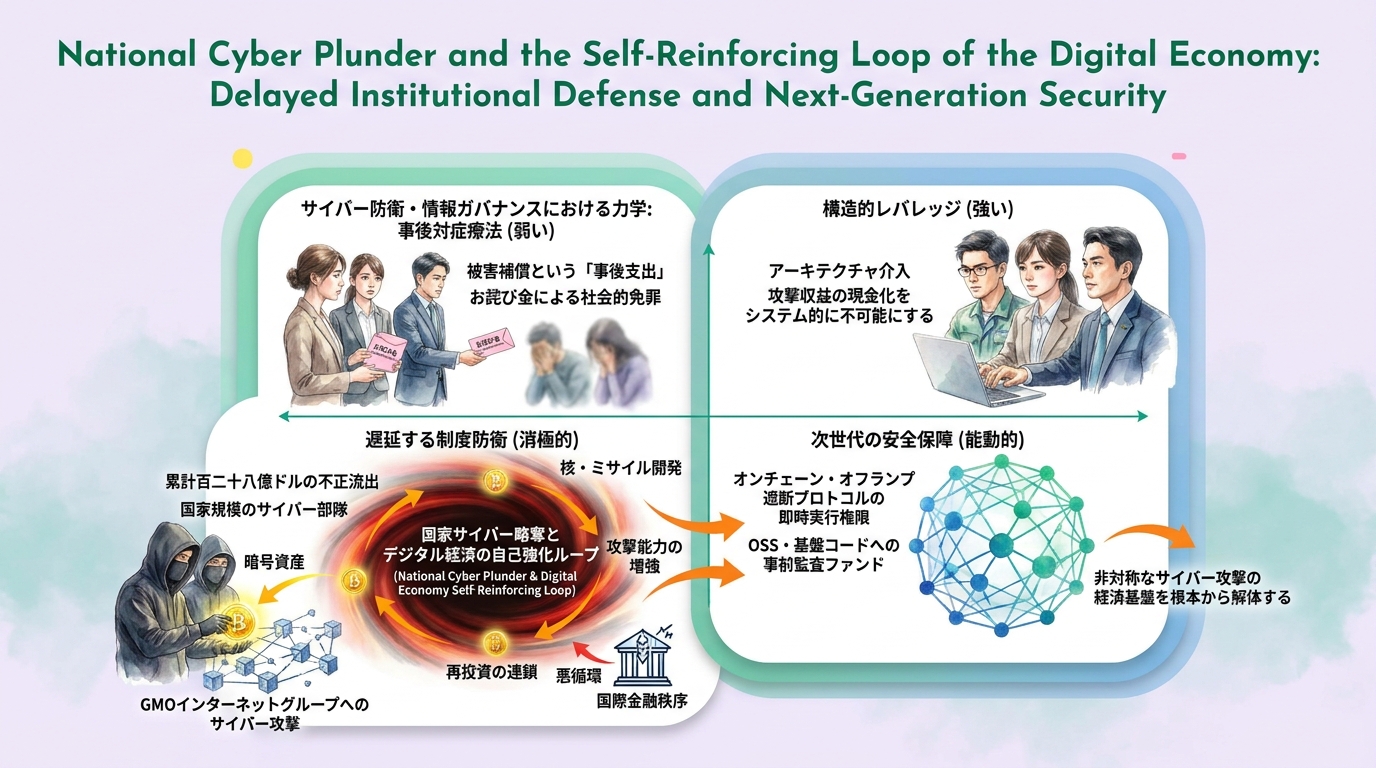
The suspected intrusion into GMO underscores the harsh reality that targeted attacks are penetrating the deeper layers of private financial and IT hubs. The cumulative $12.8 billion in cryptocurrency losses is not a collection of isolated, opportunistic breaches. From social engineering campaigns directed at target employees to smart-contract vulnerability audits and the compromise of cross-chain bridges connecting disparate blockchains, operations are executed according to meticulously organized blueprints. Targets have expanded from centralized exchanges to mainstream financial platforms, normalizing tactics that slip past defensive monitoring grids to instantly extract hundreds of millions of dollars through minor technical gaps.
The gravity of this architecture lies in a self-reinforcing loop operating within a closed circuit. Stitched together via complex money laundering routes through mixing services and decentralized exchanges, illicitly drained cryptocurrencies are repatriated to sanctioned states as hard currency. These funds are not merely allocated to ballistic missile and weaponry development; they are reinvested to nurture next-generation cyber warfare units and procure sophisticated zero-day vulnerabilities. A feedback loop has formed wherein each success sharpens the precision of subsequent targets, enabling even larger capital extraction. This capital circulation, operating with temporal lags that consistently outpace defensive countermeasures, is the root cause perpetuating sanctions evasion and continuously elevating the sophistication of the attacking organizations.
The decisive choke point for dismantling this chain system is none other than the blockade of 'off-ramps'—the cash-out portals converting cryptocurrencies into real-world fiat currencies. No matter how vast a balance accumulates on decentralized blockchain ledgers, actual settlement instruments such as the U.S. dollar or Chinese yuan remain indispensable for procuring foodstuffs and dual-use materiel. Currently, North Korean-affiliated groups seek liquidation through small-scale exchanges in third-party nations with lax sanctions enforcement, underground banking networks, and over-the-counter (OTC) brokers. International financial communities must enforce strict Know-Your-Customer (KYC) standards across all exchanges and implement rigorous anti-money laundering measures, physically and technically sealing off cash-out pathways from suspicious wallets to deliver the primary intervention capable of severing this capital circuit.
However, localized responses—such as individual corporations or single nations reinforcing their own bulwarks—merely produce the side effect of shifting targets toward surrounding, vulnerable entities. Attackers invariably scout the regulatory and defensive weak points within the global financial system, using them as footholds to erode the broader structure. With private infrastructure effectively stationed on the front lines of inter-state conflict, frameworks focused solely on individual corporate accountability cannot stem the tide of massive capital outflows. Only through multilateral cooperation—where blockchain analytics firms, financial institutions, and major national security authorities share cryptocurrency transit routes in real time and tightly encircle cross-border liquidation networks like a mesh—can this vicious cycle binding weaponry to cybercrime be finally halted.