Terminals Poisoned at the Factory: The 1.3 Million-Device Hijack Exposes the Achilles' Heel of Supply Chains
The Shadows of Embedded Backdoors and Cross-Border Traffic: Transnational Crime Shaking Hardware Sovereignty
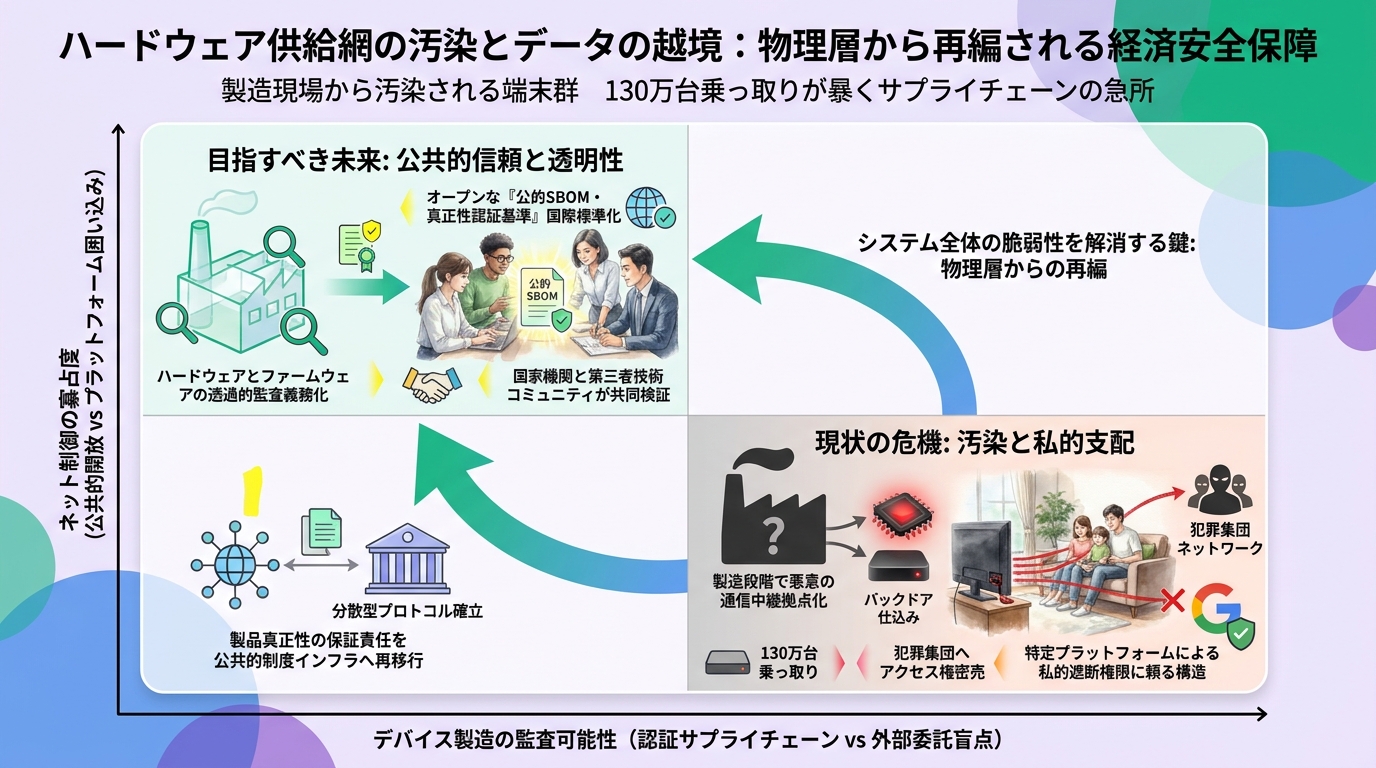
What has been brought to light is the reality that the very hardware manufacturing processes of consumer edge devices are intertwined with an illicit marketplace. More than 1.3 million targeted TV terminals had backdoors pre-installed deep within their firmware to relay and control unauthorized communications. Almost immediately after users completed their initial setup, these devices transmitted and received suspicious packets in the background, serving as cover for cyberattacks and routing unauthorized traffic. Although Google's large-scale domain neutralization measures and cooperation with the National Police Agency managed to sever these communications, completely neutralizing the physical hardware deployed in individual homes remotely remains exceedingly difficult, leaving behind the heavy and complex challenge of recovering compromised equipment.
The structural linchpin of this threat lies in the countless contract manufacturing plants spread across the fringes of global procurement networks. In consumer electronics and IoT markets driven by fierce price competition, the pursuit of cost reduction has led to firmware implementation and board design being outsourced to external subcontractors, creating a blind spot where ordering parties fail to conduct adequate audits. Attackers do not even need to deploy sophisticated external hacking techniques; by simply embedding malicious code directly into firmware at the factory floor, they can flood the globe with unauthorized nodes disguised as genuine product-authenticated devices. Furthermore, because these compromised terminals function as multi-layered pivoting nodes to conceal the attackers' locations—as noted in tracing investigations of cyberattacks targeting domestic infrastructure firms—it creates a cascading effect where determining the masterminds hiding overseas through IP address analysis alone becomes nearly impossible.
The contamination of the physical layer and the expansion of cross-border illicit traffic fundamentally shake the frameworks of intergovernmental jurisdiction and economic security. Just as cross-border investigations are prolonged and the limits of international cooperation are exposed in attacks on domestic IT giants—where operating hours point toward Asian state-backed actors—cybercrime staging grounds are intentionally placed in judicial vacuum zones beyond the reach of legal remedies. Moreover, when hardware components and chipset production facilities are concentrated in regions fraught with geopolitical risk, site inspections and transparency are blocked by the wall of national sovereignty. While mega-platform enterprises block cross-border communications as private defensive measures, national law enforcement agencies remain bound by sovereign borders, forcing a fundamental restructuring of public-private cooperative frameworks in supply chain defense.
In an environment where hardware can be compromised before it even leaves the factory, traditional security philosophies that rely solely on 'pre-shipment checks' are no longer tenable. From component procurement, board assembly, and factory line inspections to cryptographic signing at dispatch, institutional frameworks must enforce end-to-end supply chain integrity verification capable of tracking every manufacturing stage. Simultaneously, the principles of zero trust—verifying every device as a potential threat continuously—must be extended down to the physical hardware layer, even within home networks and corporate edge devices. Rectifying the structure of trading physical infrastructure safety for short-term procurement cost reductions and hastily legislating strict procurement standards to vet manufacturer transparency has become an urgent imperative.